⭒ Bug Bounties Can’t Outbid Nation-States, but We Can Pay in Other Ways
Some friends at Hacktron were kind enough to loop me in on their HEIF Heist, and, yeah, when I say I've had a sufficiently weird summer, it's now a sufficiently weirder summer-going-into-fall. :)
"What does that mean?" you say.
To put this in plainer words: have you ever wondered how you can hack into OpenAI with an image library? For details, I'll hand it over to LiveOverflow, who I watched religiously at fifteen, to explain this: How OpenAI got hacked with an image.
His videos are still how I'd want anyone to learn security stuff and understand the security industry.
(Brief second while I nerd out)
I specialized in heap pwn back when I did CTFs, which is why I find this remarkable. Writing a reliable heap exploit used to be the kind of thing that consumed a sizable amount of waking hours, and that was with a local copy of the target + exact Docker image running on your machine.
And now, wow, an AI agent with a tasteful human steering it can start blind (no knowledge of the target's environment, like
libheifversion, libc version, ...) and adapt the exploit to each new company in 1-2 days!Heap pwn is a little Sisyphean in that every glibc bump invalidates what you know, which is why after being steeped deep in the dark arts of heap feng shui, I eventually wandered off to become a Rustacean and spend my time convincing CMU undergrads that memory safety is a solved problem, but I digress ;)
"...you did WHAT, and you only got $6.5k?"
The payout was $6.5k, and, after accounting for the ~$3k spent in Codex + Claude subscriptions to get the PoC... woohoo maths, that leaves... ~$3.5k in take-home.
And yes, on behalf of the security community, our friends on Twitter are indignant that this $6.5k is disproportionate relative to what was at stake, and wield this as a rallying cry to properly compensate security researchers for security work.
When you look at the amount of sensitive info you could've leaked from this finding, this taking over of an OpenAI employee account, and the internal codebases and Slack attachments and emails...
...what would be a fair market value for a vulnerability like this?
I should say upfront that I'm not a neutral party. I know the people involved and saw enough of the disclosure process to have opinions about it, and of course that would make me more prone to saying, yeah, please, give more money because this is good work, money good.
that said,,
I don't think one has to share my biases to see that $6.5k is modest. I would put it on the order of millions of dollars, however much a nation-state actor would be willing to pay to buy it off the researcher.
But also, from the POV of the bug bounty program
Before we pull out the pitchforks on OpenAI, let's think from OpenAI's POV, right? The bug bounty program is allocated with a fixed budget. If OpenAI paid out true market value, they'd be dangling a juicy steak in front of every researcher on the planet, and their bug bounty program would go bankrupt prrrrretty soon.
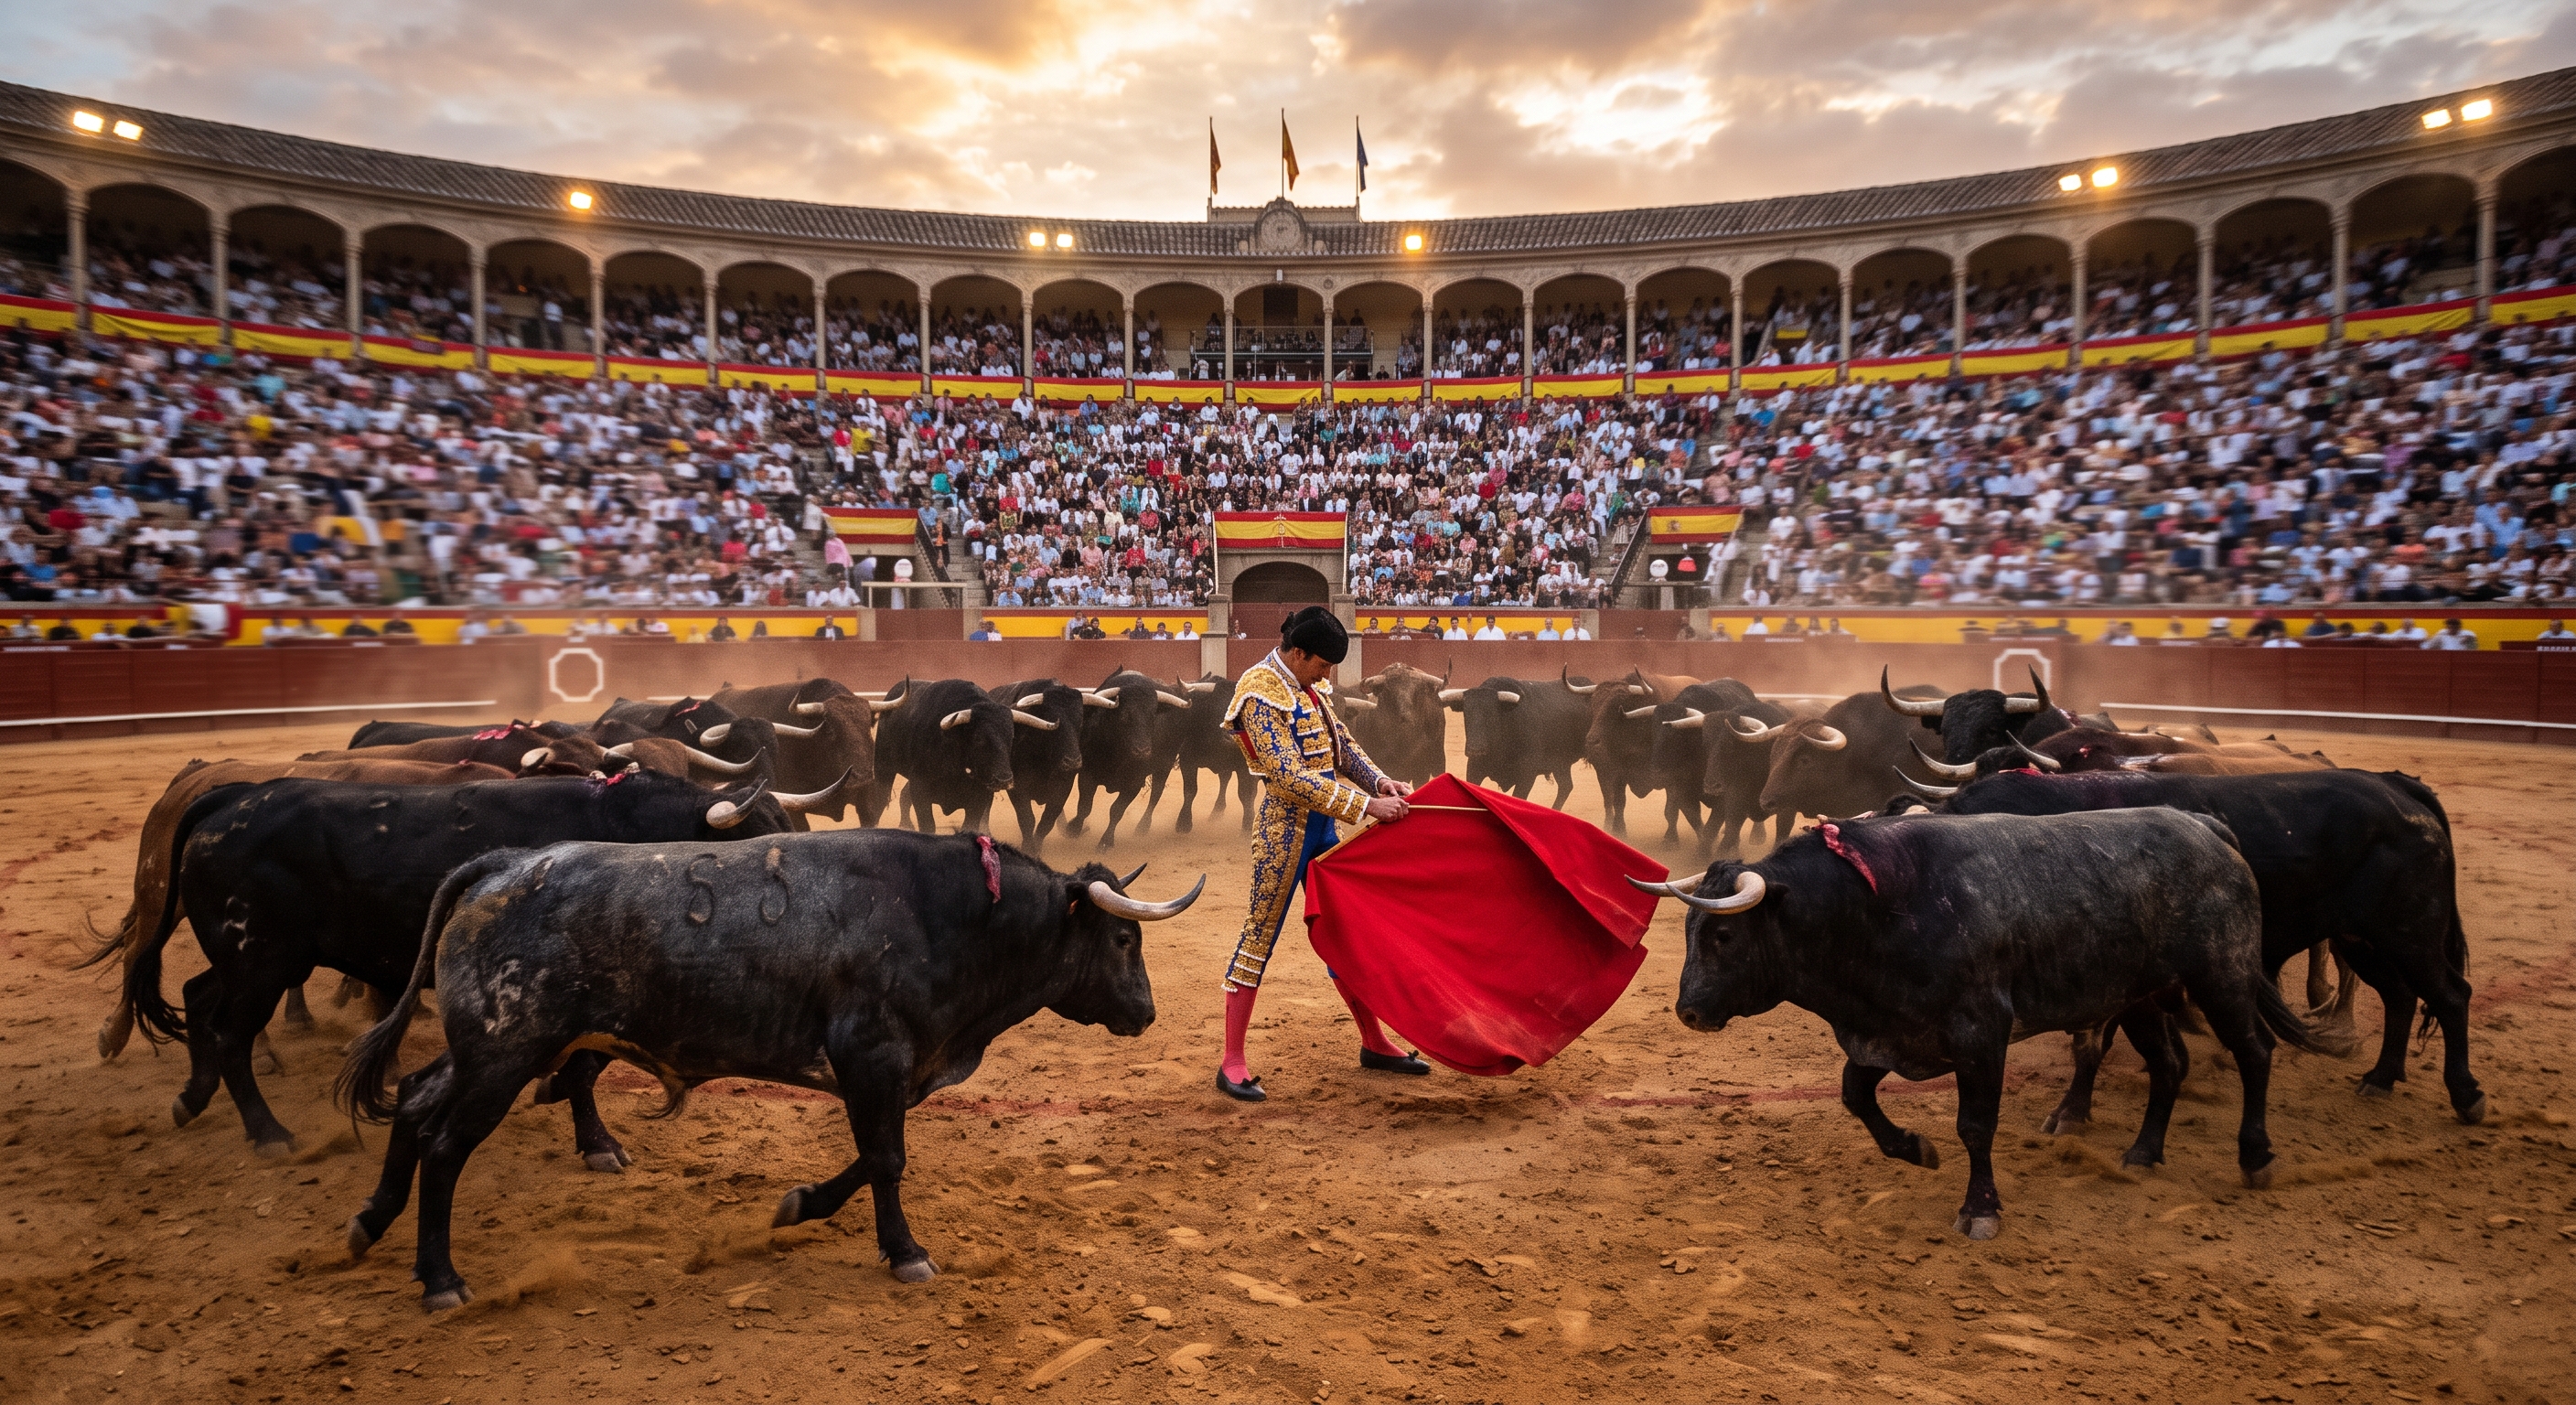 "Hi bulls, I mean, security researchers, I've proven I'm vulnerable and I pay millions and zillions, very juicy steak, very very juicy steak, and there's more where that came from!! (and yes I'm aware you're all herbivores!)"
I worked on Meta's security team for a time, and I spent my time there more of a blue-team-y role, which rounded out the half-formed picture that I originally had from doing red-team-y things. At the time I really wanted to transfer to a red-team-y team, but in retrospect, I needed the other half of the perspective more than my desire for the fun half.
One thing I didn't expect was that on the defensive side you sort of graduate out of seeing exploits as an artform (where you appreciate a bug for its technical beauty) and into more policy and governance-esque work.
A lot of what we actually dealt with day to day was policy and governance stuff or org-level blockers like which team owns what and who has to sign off on what.
And, one thing that stuck with me from that time, from my interactions with bug bounty, was that not all targets were treated equally. Bug bounties were priced relative to how much money the bug could lose the company, which meant that a bug in our ads platform was worth far more than a bug in some research library/framework that only touched ML training repos, or some old fart admin tool, even though all three bugs were equally gorgeous from a pure research standpoint.
And the other constraint was capacity, that these programs receive a crap-ton of reports, most of them low signal / duplicates / false positives, and there are only so many human-hours to triage them.
Even from this lens of "price the bug by $$$ lost," I felt a little strange about the fact that even the most impactful bugs got payouts that didn't come close to the damage that they averted. These guys found a bug in the Ads Platform that would've cost the company millions of dollars, and they walk away with a couple hundred / thousand bucks?
Every time this happened, I would wonder, "Wow, these people are superhumanly well-adjusted. There must be something that keeps them on the boring, good side instead of all the other things they could've done with this finding."
In spite of all of this, I'm sympathetic to the people running these bug bounty programs. You have a fixed budget and many reports to go through, and most of the decisions that the program makes are the ones I'd make too.
And (anecdotally) this might be why, prior to AI, it was popular for some of my friends to end up doing security work in web3 because the impact is relatively easy to quantify in dollars lost, e.g. "this would have drained $40M from the protocol," and web3 companies are much more willing to pay researchers lucratively for their work.
See Luna Tong's The Auditooor Grindset, one of the earliest manifestos to talk about this. It's aimed at underpaid vulnerability researchers and encourages them to look at crypto as greener pastures. That yes, crypto is broken and kind of degen, but they need not believe in it to audit it, and none of that is a reason to leave money on the table.
Bad Exchange Rates
So, given that paying bugs by true market value is unsustainable on a fixed budget, I see the pricing market for bug bounties not so much as a price-discovery situation where the company has to clear the price of the highest bidder, and more as a goodwill-retention situation.
That is, we pay, in money and other sorts of currencies, such that the upside for responsible disclosure outweighs the downsides of selling it elsewhere (and there can be many, like legal and social risk).
This brings me to Leila Clark's essay What are you getting paid in?, which influenced my career decisions during a very formative time of my life.
Her argument expresses a pretty universal sentiment that money is not the only thing we optimize for, but what made it memorable to me was her choice to describe these things as currencies.
my manager friend wanted to point out that you can pay people in lots of currencies. Among other things, you can pay them in quality of life, prestige, status, impact, influence, mentorship, power, autonomy, meaning, great teammates, stability and fun. And in fact most people don’t just want to be paid in money — they want to be paid some mixture of these things.
...and the part that was super memorable to me, that elevated it above the usual "money isn't everything" platitude, is her observation that these currencies don't convert cleanly:
... There’s an exchange rate between many of the currencies you can get paid in, but it’s pretty bad. You can sort of buy coolness with money through philanthropy, but it’s very expensive. You can sort of turn power into money (and money into power), but you have to be careful about it if you don’t want to go to prison for corruption. In general, I’ve found it’s usually easier to accumulate what you want through time and work than try to convert between currencies.
If we want researchers to keep choosing the boring "good side"
Bug bounties, viewed in this way, pay terribly in dollars while having high potential to pay well in many other things.
And this is a pretty big deal, because the worry I keep hearing is along the lines of
"if the labs pay security researchers measly amounts, they stop being on the side of good and they join the dark side!"
where dark side = sell out to nation-state actors, sell out to crypto degens, etc.
I think the premise is right, and a common conclusion people reach from here is "pay more," and I don't disagree, but this is also tricky when the security departments + bug bounty programs are allocated the way that they are.
Security budgets get set by some poor chap who has to justify them in terms of "how does this generate monies for Big Corp," and because security work explains itself as "pay out $$$ to reduce bugs," it shows up as an expense rather than a revenue-generator, and this naturally sets a ceiling far, far below what the bug is worth. :')
Our bug bounty programs can't really win against those nation-state actors by paying more.
So, if money is a currency that we're unable to compete in, let's think through the ones we can. Off the top of my head...
Pay in recognition. Let people publish and credit them by name! Most security researchers don't have many lines into mainstream press, so make the introduction if you can, and help them represent the field faithfully. And, not calling out anybody in particular, don't tie up the writeup in lengthy legal negotiations.
Notice that Hacktron's $6.5k monetary payout is, at this point, moot relative to their reputational payout, and now they have established themselves as credible operators in the space ("the guys who hacked OpenAI") and people know to go to them for security problems.
Pay in not being treated as the enemy. I am consistently surprised by the scope disputes and the legal saber-rattling over a PoC. However sympathetic I am to the person on the receiving end (it's an awful, anxiety-inducing feeling, and the first instinct is to establish that this wasn't supposed to be possible), the posture you show them should be that these researchers are doing you a favor.
Pay in mentorship, and make sure there's still young'uns left to mentor. Speaking personally and also in the shoes of many others, when you figure out something nonobvious/tricky/time-consuming, it feels really good to teach others how you did it. (I would not have gotten into this if not for the people posting high-quality, free explanations on their blogs and on YouTube.)
I worry that security research might lose its junior pipeline under unfavorable conditions. Speaking anecdotally, most of the CTF friends I know have drifted into adjacent fields that use a similar CS/systemsy skillset — infra, ML, crypto, quant trading, and the ones still working in security are real troupers. This is not because we stopped loving the work, but because the work burns people out and pays poorly relative to the other jobs that our skillset opens up.
So we should make sure that juniors entering this field still receive adequate mentorship and pay, and that the people senior enough to teach still have the incentive and a reason to stay in the field long enough to do it. Especially with AI making it easier to attack software, we really should have more people valuing security, not less.
And obviously, also, pay in money. The above currencies, of course, don't pay the bills, and Leila Clark's point about bad exchange rates applies here, that you can't convert coolness and recognition and mentorship into a mortgage payment any more cleanly than you can convert money into coolness.
So my argument isn't that we can stop paying researchers in favor of extra high-fives and fist-bumps (please don't strawman me like this :P), but rather that we should offset what a fixed bounty budget can't cover by adding in the currencies above, while also advocating for more budget towards security.
Encouragingly, at least anecdotally, the bar for keeping the good guys on the boring good side so far seems lower than the doom-posting suggests. Being respected and treated well is not a substitute for being paid well, but it does seem to be doing a lot to keep people on the boring good side so far. It also doesn't take much from our day, so maybe let's do that while we advocate for the budget to go up anyway.
I don't have a fully formed policy proposal yet, but I think it would be productive to open the floor towards the currencies in which we can pay for high-quality security work.